
Quick Answer
Agentic AI, Pindrop, and Anonybit serve different roles in voice security. Pindrop offers synthetic-audio detection and AI-caller detection capabilities for supported environments. Anonybit has previously announced decentralized biometric and identity-bound AI-agent solutions. A combined architecture should be treated as a proposed design until product availability and integration compatibility are verified. Effective deployment requires independent identity checks, controlled permissions, and safe escalation procedures.
Introduction
Agentic AI, Pindrop, and Anonybit address different parts of a growing enterprise security challenge: detecting synthetic voices, verifying identities, and controlling what automated systems are authorized to do. Understanding those differences is essential before an organization considers combining these technologies.
Pindrop develops voice intelligence and deepfake detection technology. Anonybit has published an approach to decentralized biometrics and identity-bound AI agents. An AI orchestration layer can coordinate verification signals, apply security policies, and escalate uncertain cases.
These capabilities could contribute to a layered voice-security architecture. However, they should not be treated as a single, verified product integration without current vendor documentation confirming compatibility.
This guide examines the technologies, explains how a proposed architecture could work, and provides a practical evaluation framework for CTOs, CISOs, fraud leaders, and enterprise security teams.
Research reviewed October 15, 2026.
What Are Agentic AI, Pindrop, and Anonybit?
Agentic AI: Coordinating Security Decisions
Agentic AI describes AI systems that can pursue goals through sequences of actions, tool calls, and decisions rather than simply generating a response to a prompt.
For a broader discussion of enterprise AI governance, see our guide to AI governance and human oversight.
In an enterprise security workflow, an agent might gather risk signals, request additional authentication, open a fraud investigation, or send a transaction for human approval.
The security challenge is that an autonomous system can make an incorrect decision or exercise permissions beyond what its task requires. Its ability to act must therefore be constrained by explicit authorization rules, access controls, and audit requirements.
For voice-fraud prevention, the appropriate role of an AI orchestrator is to coordinate trusted security services and apply an approved decision process—not to invent its own authentication standards.
Pindrop: Voice Intelligence, Deepfake Detection, and AI Caller Detection
Pindrop provides enterprise technologies for evaluating risk in voice and other real-time interactions. Two products are particularly relevant to this topic.
Pindrop Pulse addresses synthetic audio and video detection. Its meeting-security offering also describes continuous identity evaluation, passive voice authentication, and location-risk signals. The exact capabilities depend on the product and supported deployment.
Pindrop BotStopper, launched on September 16, 2026, focuses on identifying AI and automated callers in contact-center environments. Pindrop says the technology operates in real time and checks against more than 5,000 registered AI voices in its intelligence network.
Sources: Pindrop Pulse for Meetings and Pindrop BotStopper.
These capabilities address related but distinct questions:
- Does the audio or video show signs of synthetic manipulation?
- Is the caller a human or an automated AI system?
- Does the broader interaction contain risk signals that warrant additional investigation?
Detecting an AI caller is not the same as detecting a cloned human voice. Likewise, detecting a deepfake does not, by itself, establish the real-world identity of the speaker.
Security teams should select the relevant Pindrop product based on their threat model rather than assuming every product performs every function.
Anonybit: Decentralized Biometrics and Identity-Bound AI Agents
Anonybit has described a decentralized biometric architecture intended to reduce dependence on centralized stores of sensitive biometric information.
Its published material also describes identity-bound AI agents: systems designed to connect agent actions with an authenticated identity, authorized permissions, and auditable workflows.
In May 2025, Anonybit announced a solution developed with SmartUp for identity-bound AI-agent workflows. The announcement described use cases involving payments, supply chains, and order management.
Source: Anonybit and SmartUp identity-bound AI-agent announcement.
The distinction is important. Anonybit’s proposed role in this architecture is not simply to detect deepfake audio. It is to contribute to identity verification and privacy-oriented identity infrastructure.
Organizations must confirm current product availability, supported biometric modalities, integration requirements, and contractual terms before relying on a specific deployment.
A decentralized approach can reduce particular risks associated with centralized biometric storage. It does not automatically eliminate every security risk or guarantee compliance with applicable privacy laws.
How Could Agentic AI, Pindrop, and Anonybit Work Together?
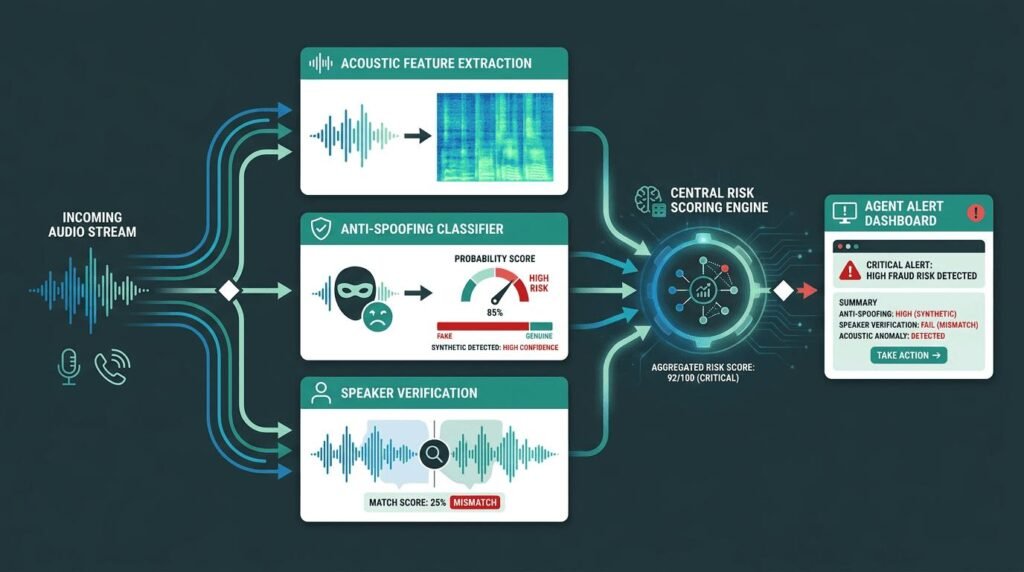
The following is a proposed architecture, not a claim that Pindrop, Anonybit, and a particular AI orchestration framework have a ready-made joint integration.
1. Detect suspicious voice or automated-caller activity
The relevant Pindrop product evaluates the supported voice or media interaction and produces the signals available through that deployment.
For example, a suspicious synthetic-audio signal or an unexpected automated caller may trigger further investigation.
The application must use the actual signals and outputs supported by the selected product. Do not assume that every product exposes the same scores, APIs, or real-time events.
2. Verify the identity behind a sensitive request
If the risk policy requires stronger identity assurance, the workflow invokes an approved authentication method.
An Anonybit-based deployment could be considered where its available biometric and identity capabilities fit the use case. The organization must first validate enrollment, matching, system compatibility, fallback procedures, and current availability.
The identity check must answer the appropriate question: is the person or identity authorized to make this particular request?
A voice that sounds authentic is not sufficient proof of authorization. Nor does successful biometric matching automatically make a transaction legitimate.
3. Evaluate the surrounding context
The orchestration layer collects the relevant signals available to the application, such as:
- The result of voice or automated-caller detection.
- The outcome of identity verification.
- The type and value of the requested transaction.
- Whether the requested action is within the user’s authorized permissions.
- Whether the transaction violates an established business rule.
Only authorized, necessary data should be included. Access to sensitive customer or employee information must remain subject to the organization’s existing permissions and privacy requirements.
4. Apply a controlled security policy
The application evaluates the available results against predetermined rules.
| Outcome | Example response |
|---|---|
| Requirements satisfied | Continue the authorized workflow. |
| Additional evidence required | Request an approved, independent authentication factor. |
| Signals conflict | Escalate for human review. |
| Mandatory security rule violated | Reject or suspend the requested action. |
| Detection or verification unavailable | Use a predefined fail-safe procedure. |
The AI orchestrator may recommend or coordinate the next step, but it should not override mandatory controls. High-risk actions should require the approval and authentication specified by the organization’s security policy.
5. Record the evidence and decision
Maintain an appropriate audit trail showing which checks were performed, which policy applied, what action was taken, and whether a human intervened.
Protect these records with access controls and retention policies. Avoid collecting raw audio, biometric material, or other sensitive data unless it is necessary and appropriately protected.
The result is a security workflow that can explain its decisions rather than relying on an opaque AI-generated approval.
Pindrop vs. Anonybit vs. Agentic AI
These technologies should not be compared as interchangeable products. They serve different purposes within a potential security architecture.
| Capability | Pindrop | Anonybit | Agentic AI orchestration |
|---|---|---|---|
| Primary role | Voice intelligence, deepfake detection, and supported caller-risk detection | Decentralized biometric and identity infrastructure | Coordinating actions and enforcing workflow logic |
| Main security question | Does this interaction show suspicious voice or automated-caller signals? | Can the relevant identity be verified using a supported method? | What action is permitted given the available evidence? |
| Identity verification | Product-dependent capabilities | Identity and biometric capabilities depend on the deployment | Uses verification results supplied by connected services |
| Decision authority | Provides technology and signals within its product scope | Provides identity-related capabilities within its product scope | Should operate within predefined authorization rules |
| Key implementation concern | Detection performance and supported channels | Availability, biometric modality, privacy, and integration | Permissions, reliability, policy enforcement, and auditability |
Practical takeaway: Pindrop’s detection functions and Anonybit’s identity infrastructure could be complementary, but compatibility between the particular products must be established. The orchestration layer coordinates the workflow; it does not replace either function.
Example: Protecting a High-Value Payment Request
Consider a hypothetical bank contact center receiving a call requesting a high-value payment to a new beneficiary.
For related considerations around transaction workflows and payment infrastructure, see our guide to SaaS payment-processing features.
The caller sounds familiar and provides the correct account details. However, the voice-risk system returns a suspicious result.
A poorly designed workflow might immediately approve the request because the caller passed knowledge-based questions. An alternative is to use a layered policy:
- Evaluate the voice interaction using the supported detection service.
- Request additional identity verification through an approved method.
- Check whether the payment complies with transaction limits and authorization rules.
- Escalate contradictory evidence to a fraud analyst.
- Release the payment only when the required controls have been satisfied.
Suppose the identity check succeeds but the voice interaction remains suspicious. That does not automatically mean the request is fraudulent, nor does it justify ignoring the detection result.
The appropriate response depends on the bank’s approved policy, the transaction’s risk, and the available independent evidence.
This hypothetical illustrates why a high-risk workflow should combine detection, identity assurance, transaction controls, and human oversight instead of relying on one score.
Implementation Roadmap for CTOs and Security Teams
Step 1: Define the use case and threat model
Document which workflows require protection. Examples include contact-center account recovery, financial approvals, sensitive account changes, and high-risk virtual meetings.
Identify relevant threats, including synthetic voice impersonation, automated callers, compromised credentials, replay attacks, and social engineering.
Not every threat requires the same product or authentication method.
Step 2: Validate current vendor capabilities
Request current technical documentation for the exact products under consideration.
For Pindrop, confirm the selected product, supported communication channel, available signals, integration interfaces, and operational requirements.
Use our AI SaaS product evaluation criteria to assess vendor capabilities, deployment requirements, and integration fit.
For Anonybit, independently verify product availability, the supported biometric modalities, enrollment and verification methods, deployment model, and any required integration partners.
Do not assume that an API, SDK, SIPREC stream, WebRTC connection, or ready-made connector is supported unless the vendor confirms it.
Step 3: Map the identity and data flow
Document where audio or biometric information enters the system, which services process it, what results are returned, and which components retain records.
Determine which party controls each data flow, how failures are handled, and how sensitive information is protected.
A proposed architecture diagram should distinguish verified vendor functions from integration components that still need to be built or validated.
Step 4: Establish policy before granting AI permissions
Define which actions the orchestration layer may perform autonomously and which require additional verification or human approval.
Use least-privilege access, transaction limits, explicit authorization checks, and a deterministic enforcement layer for mandatory security requirements.
Do not allow an AI agent to expand its own privileges or bypass a required approval simply because its reasoning suggests the action is safe.
Step 5: Run a controlled pilot
Test with representative legitimate interactions, varied audio quality, authorized synthetic-media samples, automated callers, and realistic transaction scenarios.
Evaluate:
- False-positive and false-negative rates for the relevant detection system.
- Authentication success and failure rates.
- End-to-end latency and service availability.
- The frequency of step-up authentication and manual escalation.
- User abandonment, operational cost, and fraud-investigation workload.
- Failure behavior when a vendor service or integration component is unavailable.
Document the test dataset, methodology, conditions, and results. Distinguish vendor-published benchmarks from results measured in your own environment.
Step 6: Validate privacy and regulatory requirements
Biometric information requires careful handling. Review applicable data-protection laws, consent and enrollment requirements, data minimization, retention, security controls, and user rights with appropriate legal and privacy professionals.
Organizations working under a specific digital-identity standard should also check that standard’s requirements. For example, NIST SP 800-63-4 includes a restriction on voice-based biometric comparison within its covered digital-identity authentication framework. That requirement should not be confused with the use of software to detect synthetic audio for fraud analysis.
Source: NIST SP 800-63B, Digital Identity Guidelines.
Neither decentralized storage nor an AI orchestration framework automatically establishes legal compliance.
Step 7: Deploy gradually and monitor continuously
Start with a limited deployment, review failures, and adjust thresholds only through an approved, evidence-based process.
Monitor changes in legitimate-user behavior, detection performance, latency, vendor functionality, and emerging attack patterns.
Maintain incident-response procedures and a documented fallback for uncertain or unavailable verification results.
Risks and Limitations
False positives and false negatives
A legitimate interaction may be flagged, while a synthetic or manipulated interaction may evade detection. These risks affect customer experience and security differently, so they should be measured separately.
Provide a secure alternative verification path for legitimate users who cannot complete a check.
Integration uncertainty
A conceptual architecture does not establish that every proposed component can exchange the required signals. Unsupported interfaces, differences in data formats, or deployment limitations may prevent a direct integration.
Obtain written vendor confirmation and test the end-to-end workflow before making operational claims.
Biometric privacy
Decentralization can reduce reliance on a single biometric repository, but it does not remove all risks involving unauthorized access, data handling, consent, retention, or implementation mistakes.
An agent may misinterpret a risk signal or initiate an inappropriate action. Restrict its permissions, validate its inputs, retain decision logs, and enforce critical controls outside unconstrained model reasoning.
Performance assumptions
There is no verified end-to-end latency result for this proposed three-component architecture in the evidence reviewed for this guide. Measure the complete workflow under representative conditions instead of assuming a fixed response time.
Questions to Ask Vendors Before Deployment
Before selecting or combining these technologies, ask:
- Which exact product detects synthetic voice, and which detects automated AI callers?
- What signals, APIs, SDKs, or integration methods are supported in the intended environment?
- What biometric modalities and identity-verification workflows are currently available?
- Has the exact proposed integration been implemented and tested, or is it still a design concept?
- What are the measured false-positive rates, false-negative rates, latency, and service-availability characteristics for the relevant use case?
- What data is collected, retained, transferred, or processed by each component?
- What happens if a detector, identity service, or orchestration component becomes unavailable?
- Which actions require a second factor or human approval?
- What contractual, regulatory, and operational obligations apply to each vendor?
- Can the supplier provide technical documentation and evidence supporting its claims?
These questions help an organization distinguish a feasible architecture from a marketing-level concept.
Frequently Asked Questions
Agentic AI can coordinate voice-risk detection, identity verification, and security workflows. It can request additional authentication or escalate suspicious activity for human review. Its effectiveness depends on the underlying detection systems, integration quality, and security policies.
Pindrop offers synthetic-audio detection capabilities through its supported products. Its BotStopper technology focuses on identifying AI and automated callers in contact-center environments. These are different use cases, so organizations should select the product that matches their specific threat model.
Pindrop focuses on voice intelligence and related detection capabilities, while Anonybit has described decentralized biometric infrastructure and identity-bound AI-agent solutions. Their roles may be complementary, but their products are not interchangeable and require separate capability assessments.
A combined implementation should be treated as a proposed architecture unless both vendors confirm that the specific products, interfaces, and deployment requirements are compatible. Organizations should validate the integration with both vendors before relying on it in production.
Final Verdict
Agentic AI, Pindrop, and Anonybit address different parts of the enterprise identity and voice-security problem. Their capabilities may be complementary, but the value of combining them depends on verified product compatibility, reliable detection, appropriate identity assurance, privacy safeguards, and controlled authorization.
For a CTO evaluating this approach, the best next step is to validate the required capabilities and integration paths, then measure the architecture against real operational requirements.
The objective is not to build a system that claims to detect every fraud attempt. It is to build one that handles uncertainty safely, restricts unauthorized actions, and produces evidence that security teams can investigate.
Sources and Further Reading
- Pindrop BotStopper
- Pindrop Pulse for Meetings
- Anonybit and SmartUp: Identity-Bound AI Agents
- Trust in the Age of Agentic AI: Pindrop, Anonybit, and ValidSoft
- NIST Digital Identity Guidelines
- Google Search Central: Helpful, Reliable, People-First Content
 Muhammad Talha Saeed